
For auditors
Prove every agent action.
The platform your auditor recommends to their clients. Quox is the evidence layer, not another black box: WARD is append-only, tips are signed, timestamps are RFC-3161. Give your auditors a chain they can verify themselves, with no trust in us required.
Append-onlySigned tipsRFC-3161
the agent is always watched · every action on the record
In plain words
What it is, where it lives, when to reach for it
- What is it
- The auditor’s view of QuoxCORE: the evidence trail agents leave, and how to verify it yourself.
- Where do I use it
- On an exported evidence bundle, on your own laptop, with no network and no Quox account.
- When would I use it
- When you are asked to rely on an AI agent’s work and need proof, not assurances.
- How do I use it
- Ask the operator for an evidence export, then run the offline verifier this page walks through.
QuoxCORE is the free, self-hosted platform underneath this. What is QuoxCORE
The basics
What is an AI agent audit trail?
An AI agent audit trail is the record of what an agent did, not just what it said: which tool it called, what the input was, who approved it, and what happened in response.
A useful one is verifiable, not just present: an event log an admin can edit after the fact proves nothing under audit, because the log and the actor with reason to alter it share the same trust boundary.
Quox writes that trail as VOLT: each event hash-chained to the one before, so altering any stored event breaks verification at that exact point. WARD then witnesses the chain externally, so tampering is detectable even if the host itself is compromised.
The edge that matters for an auditor: verification runs offline, against evidence exported from the platform, with no vendor account, API key or Quox involvement required. The command shown below is the same check your auditor can run on their own machine, against a file, not a live system they have to trust.
The library
The audit trail, end to end.
Every layer of the trail has its own deep dive. Start where your question lives.
The audit today
The evidence exists. Assembling it for your auditor is the expensive part.
PBC lists take weeks
Your auditor sends a 200-item request list. Your team spends weeks locating, formatting and uploading evidence across scattered systems.
Evidence is always stale
By the time you assemble the evidence package, the data is already one sprint out of date. Point-in-time snapshots miss what happened last week.
Working papers are manual
Auditors spend 40% of their time documenting what they tested and what they found, in spreadsheets rather than in the system where the evidence lives.
No trust required
Verify it yourself.
This is the receipt. As the AOCL stack processes one request, each layer writes a row hash-chained to the one before. Watch the chain build, then watch the verifier recompute every hash. Alter one byte anywhere and the chain stops matching.
receipt · one evidence row
the chain rule, straight from the store:chain_hash = sha256(prev_hash : hash : id : created_at)
verifying chain…
One request, every layer receipted. As the AOCL stack processes a request, each layer writes a row chained to the one before. Change any row and every chain hash after it stops matching.
quox ward verify --org acme --offlinethe same check, offline, on your machine · checking 4,213 blocks · 0 mutations
verifyChain(genesis → tip) → TRUE ✓ signed
Illustrative walkthrough. Verify a real, recomputable record on /verified.

Compliance tools
Six tools that assemble the paperwork from the record.
All six draw on the same chain, so the paperwork is assembled from the record of what actually happened, not rebuilt by hand.
ISO 27001 SoA Builder
Review all 93 Annex A controls: applicability, implementation status and auto-detected evidence for technical controls. Export the completed statement for your auditor.
ISO 27001:2022 · 93 controlsEU AI Act Risk Classifier
Guided questions place your AI system in its risk tier: prohibited practices, Annex I and Annex III, GPAI obligations and transparency. Produces a classification memo.
Free · no account requiredPrivacy Impact Assessment
A GDPR Article 35 DPIA with all 6 mandatory sections, an interactive 5x5 severity and likelihood risk matrix, auto-populated fields and a DPO review lifecycle.
GDPR Article 35Evidence Explorer
Select any control and see every piece of evidence that satisfies it, traced from AEE envelope to VOLT hash chain to WARD external receipt in one click.
AEE → VOLT → WARDPDF Report Engine
Auditor-grade reports whose metadata carries a WARD-signed SHA-256 manifest hash, verifiable with the same trust anchor that signs WARD tips. Nine export formats, with opt-in redaction that masks PII before signing.
WARD-signed · 9 formatsAuditor Portal
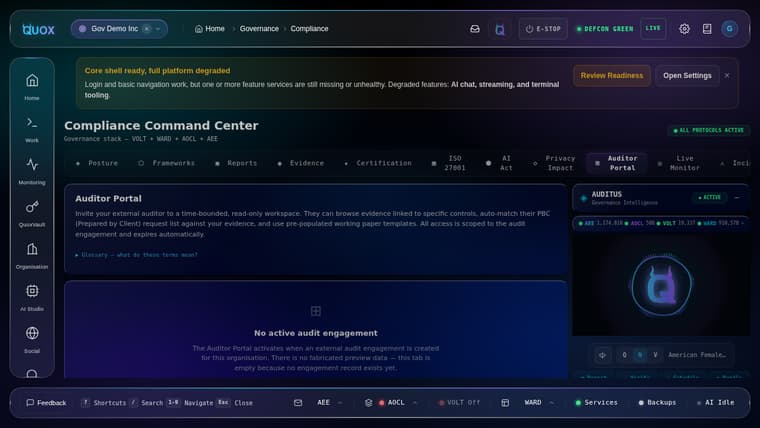
A time-bounded, read-only workspace your external auditor signs into, with PBC auto-match and pre-populated working papers. More below.
EnterpriseThe VOLT and WARD protocols and the evidence API are core. The dedicated ledger and receipt views, and the per-turn decision record, are the Decision Evidence enterprise add-on at $599/yr. See Decision Evidence →
Exports, backed by the chain: SoA mapped to the evidence that shows each control operating·DPIA drawn from what agents actually touched, and under which lease·evidence packs your auditor verifies offline with the public verifier, no account with us needed.
The auditor portal
A workspace your auditor signs into.
Stop couriering screenshots. Your auditor gets a time-bounded, read-only view of the chain: they upload the PBC list, Quox auto-matches each item to live evidence, and every working paper starts pre-populated with event counts, sample sizes and verification status. The documenting happens where the evidence lives.
portal://acme/fy26-audit · read-only · expires 14d
working papers pre-populated from the chain
verifyChain(genesis → tip) → TRUE
Always witnessed
Watched, on the record.
Every action is witnessed. Each step an agent takes, including the refusals, lands on the chain as it happens, not in a log someone could edit afterwards. Every glyph behind this panel is an action on the record.
witness · on duty
ward://witness/run-4213
the refusal is on the chain too · nothing is witnessed after the fact
verifyChain(genesis → tip) → TRUE
the evidence stream · click to run a verification pass
Compliance tools collect evidence.Native evidence from the VOLT operations ledger, not a secondary copy from API integrations
Quox is where the evidence is born.
Seven frameworks, one chain
Evidence mapping across the frameworks your auditors already require.
For auditors
Give your auditors a chain they can check.
Start with the free EU AI Act Risk Classifier. No account required. Or talk to us about an auditor review of your deployment, part of the wider Quox enterprise platform.